
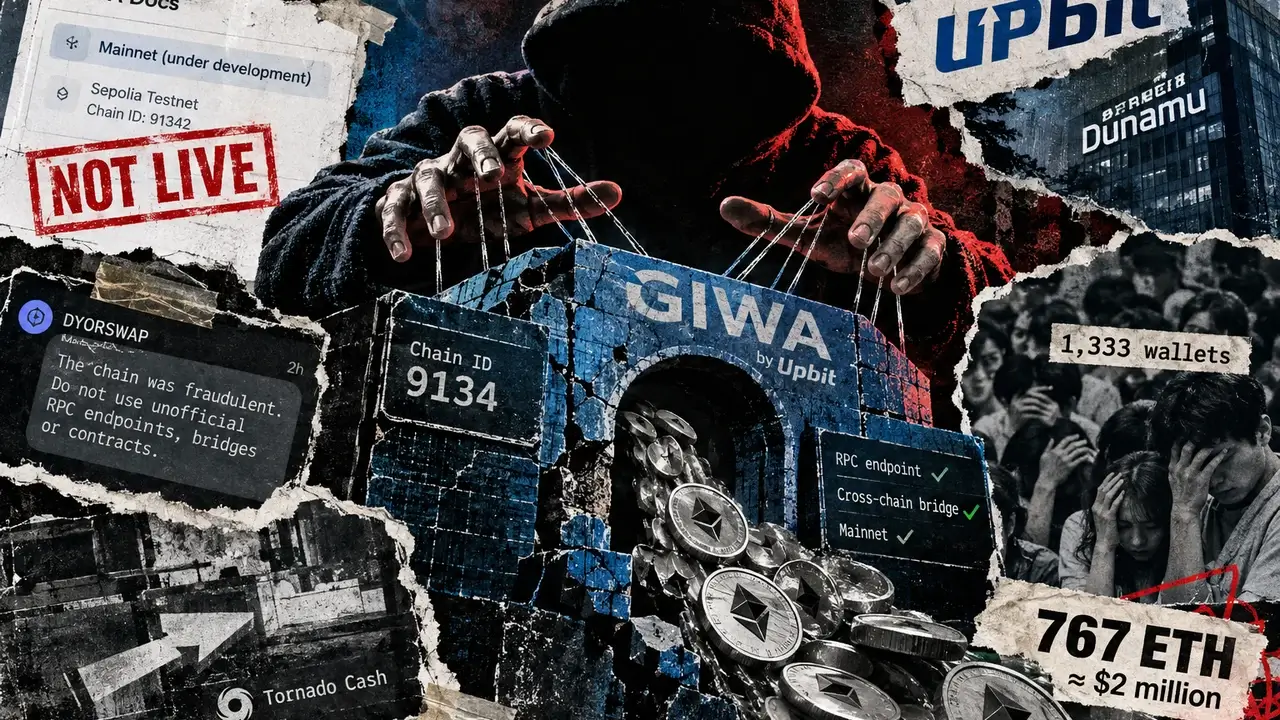
Scammers constructed a counterfeit model of Upbit-backed GIWA blockchain and lured 1,333 wallets into depositing 767 ETH, value about $2 million, earlier than draining virtually all of it.
The faux community gave the impression to be GIWA’s anticipated Ethereum Layer 2 mainnet, full with an RPC endpoint, cross-chain bridge, and Chain ID 9134, the identifier related to the deliberate launch.
However GIWA’s mainnet was not stay.
In an X submit, GIWA said claims that its manufacturing RPC had leaked have been false as a result of no mainnet RPC exists. Its documentation lists solely GIWA Sepolia, which makes use of Chain ID 91342, whereas the manufacturing community stays beneath improvement.
DYORSWAP, whose neighborhood initially interacted with the purported community, later said the chain was fraudulent and warned customers in opposition to unofficial RPC endpoints, bridges and contracts. It said:
“The faux community used the proper GIWA Chain ID (9134), which made it seem official throughout our preliminary verification. We’ve got additionally recognized particular suspicious messages and people within the associated neighborhood that could be related to this incident.”
Dunamu, operator of South Korea’s largest crypto alternate, Upbit, is developing GIWA utilizing Optimism’s OP Stack.
Dunamu and the Optimism Foundation announced in Might that GIWA is deliberate as the primary Self-Managed OP Enterprise chain, permitting Upbit to retain operational management whereas Optimism gives backup infrastructure and help.
Attackers waited for deposits earlier than altering the bridge
On-chain information suggests the attackers spent hours making ready the infrastructure earlier than the primary vital deposits arrived.
Pseudonymous blockchain analyst Stablemark said wallets tied to the operation have been funded by way of ChangeHero on Sept. 26. About 11 hours later, the Protected pockets controlling the scheme and the faux bridge went stay.
Over the subsequent 13 hours, 1,333 wallets deposited a mixed 767 ETH.
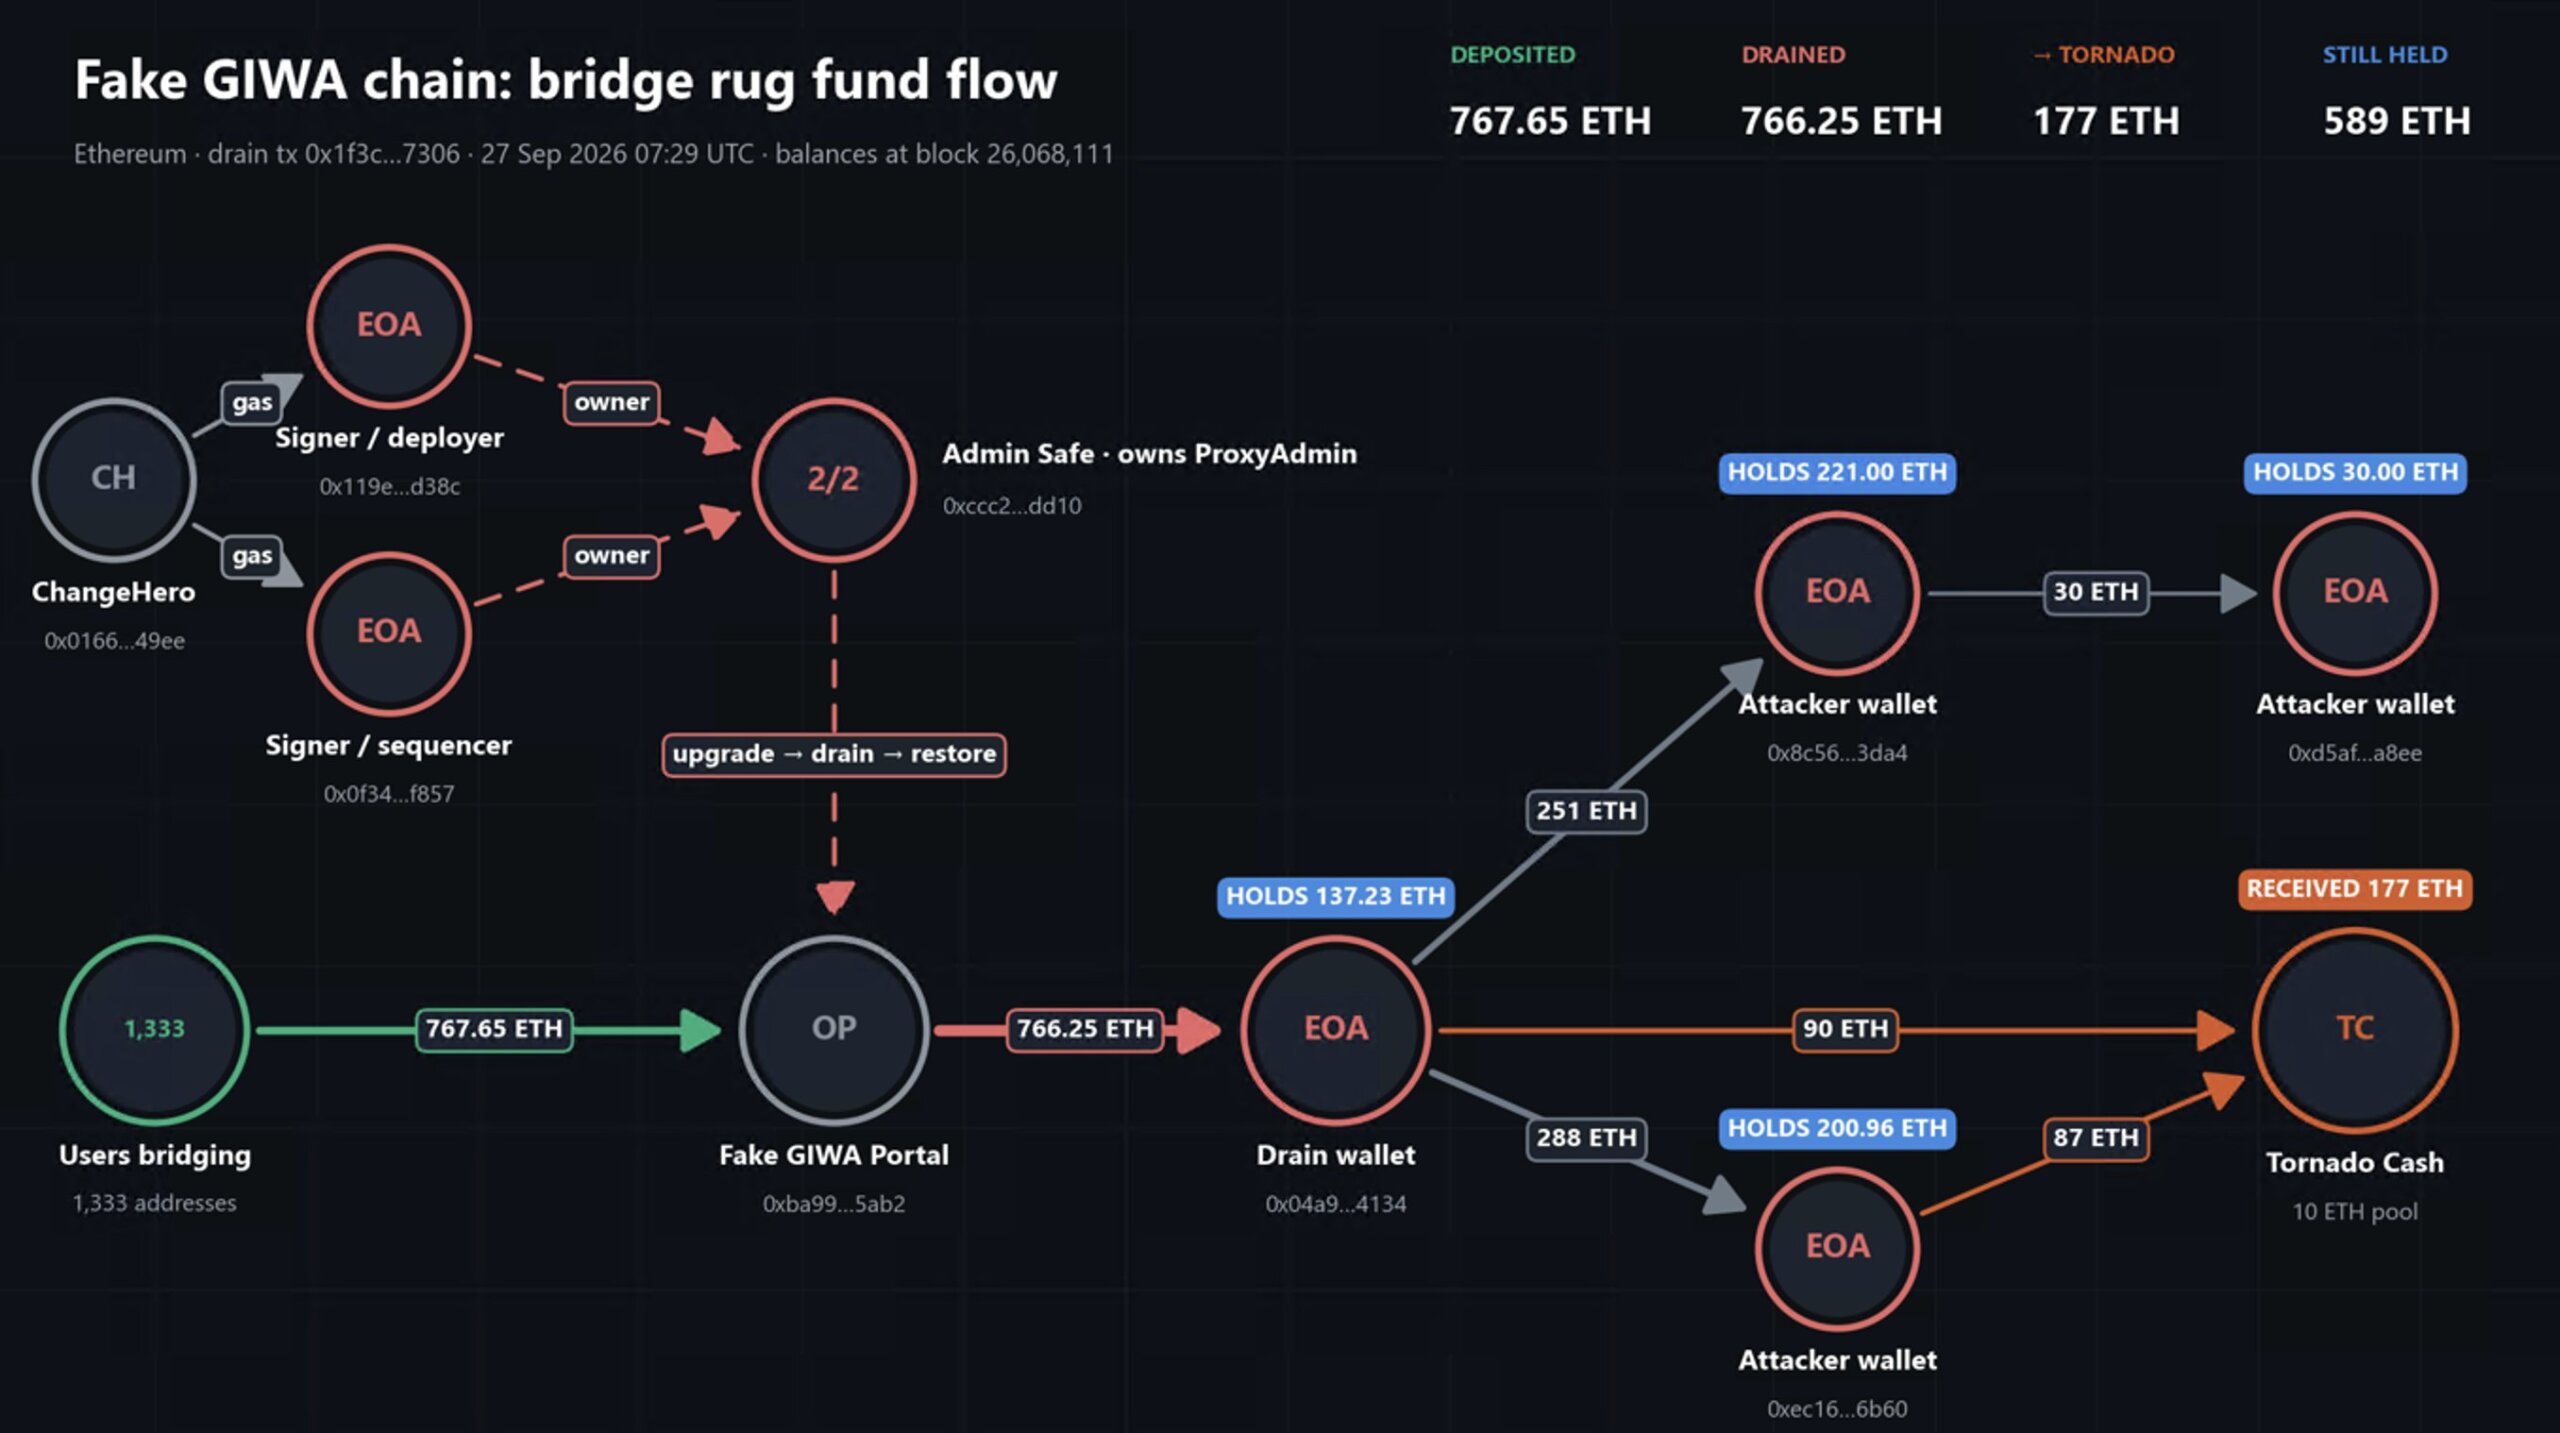
The operators then modified the bridge’s portal code and drained 766 ETH in a single transaction, in accordance with Stablemark.
The sequence suggests the bridge remained operational lengthy sufficient to build up deposits earlier than the operators changed its controlling code and eliminated the funds.
The assault relied partially on how EVM networks are recognized. A Chain ID can inform a pockets which community it’s related to, but it surely doesn’t confirm who controls the RPC endpoint or bridge behind that community.
Through the use of GIWA’s anticipated Chain ID 9134, the operators may make the surroundings seem according to the anticipated mainnet whereas retaining management of the infrastructure receiving person funds.
The stolen ETH has since begun to maneuver.
Stablemark mentioned 177 ETH was routed by way of Tornado Cash, complicating efforts to hint its subsequent vacation spot, whereas one other 589 ETH remained unfold throughout 4 wallets on the time of his replace.
That leaves a lot of the stolen funds seen on-chain for now, although additional transfers to mixers, exchanges, or different providers may slender the window for investigators to freeze or get well them.
DYORSWAP provides 40% compensation to smaller victims
DYORSWAP has moved to compensate some customers caught within the faux blockchain scheme after reviewing affected addresses.
The undertaking said wallets that bridged lower than 5 ETH would obtain compensation equal to 40% of their cross-chain quantity.
Claims involving greater than 5 ETH shall be dealt with individually and require id and deal with verification, as a result of DYORSWAP mentioned some bigger wallets could possibly be linked to phishing or different fraudulent exercise.
It additionally revealed an deal with for compensation distributions and warned victims to confirm it by way of official channels, citing the danger that scammers may exploit the incident once more utilizing faux reimbursement requests.
The compensation plan leaves substantial losses with customers even the place claims are authorized. Smaller victims would get well lower than half of what they deposited beneath the introduced phrases, whereas outcomes for bigger wallets stay topic to particular person evaluate.
DYORSWAP has mentioned it’s preserving RPC data, bridge addresses, transaction information and neighborhood communications as investigators reconstruct how the fraudulent community unfold.
