
Microsoft disrupted cryptocurrency-accepting cybercrime suppliers linked to multiple billion phishing messages worldwide this yr.
The corporate and cybersecurity group Well being-ISAC secured a US courtroom order to grab and redirect domains supporting YAM Retailer, CoGUI and Iron Man, three providers that offered accounts and phishing tools to fraudsters, in accordance with an Oct. 14 statement.
Microsoft mentioned it had disabled greater than 20,000 accounts linked to YAM Retailer and was persevering with to dam greater than 100,000 impersonation and fraud domains. Since January, the providers helped criminals ship messages concentrating on greater than 75,000 organizations throughout greater than 150 international locations, producing tens of thousands and thousands of {dollars} for his or her operators.
The investigation started after Japan’s Nationwide Police Company alerted Microsoft to scams concentrating on shoppers and companies late final yr. Investigators traced the campaigns to a Chinese language-language market the place felony teams might buy the infrastructure wanted to run phishing operations with out constructing it themselves.
YAM Retailer provided fraudulently obtained Microsoft and Google accounts, cloud sources, and internet hosting. Some operators revived expired domains belonging to nonprofits and academic organizations, then used the seemingly respectable web sites to acquire Microsoft 365 accounts for resale.
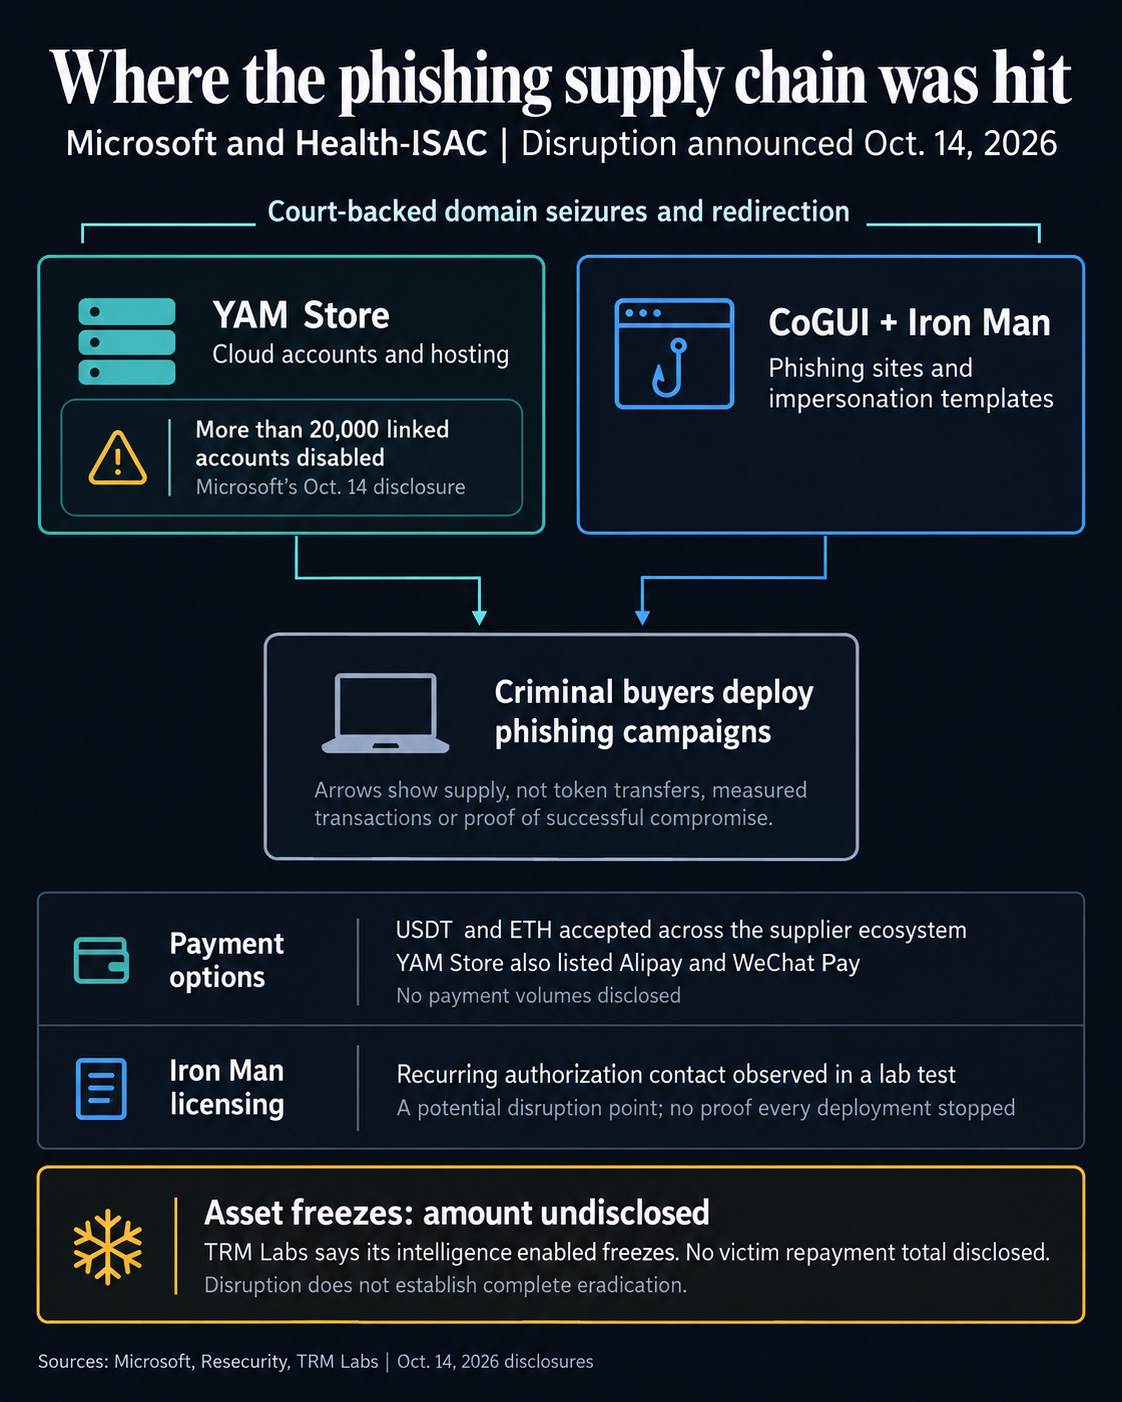
CoGUI and Iron Man provided ready-made phishing pages and messages that mimicked banks, retailers, transport authorities, and authorities businesses. Microsoft and safety agency Resecurity recognized greater than 2,300 Iron Man templates, permitting prospects to tailor scams to manufacturers and international locations.
Crypto funds and a wider infrastructure crackdown
Microsoft’s technical investigation found that the providers accepted cryptocurrency, together with Tether’s USDT and Ethereum. YAM Retailer’s storefront supported USDT on the Tron community alongside Alipay and WeChat Pay, whereas Cloudflare mentioned patrons might additionally pay for market choices with USDC.
The cost choices gave prospects a number of channels to purchase compromised credentials and phishing providers. YAM Retailer additionally maintained a sub-reseller tier, increasing the distribution of accounts and infrastructure past its personal storefront.
Blockchain analytics agency TRM Labs said its intelligence helped investigators find belongings linked to the group and freeze them. The corporate didn’t specify the worth of the frozen belongings, leaving the operation’s speedy monetary injury unclear.
The enforcement effort additionally focused providers criminals used after making their purchases. Cloudflare said it suspended accounts, disabled Employees tasks supporting phishing pages, and banned tons of of related domains and tasks. It positioned warning pages in entrance of malicious hyperlinks the place it could not seize domains.
Microsoft additionally recognized a dependency in Iron Man’s subscription enterprise: prospects purchased entry to phishing software linked to a vendor-controlled licensing server. Disabling that infrastructure might intrude with prospects’ capacity to make use of bought kits, even when copies remained in circulation.
The crackdown concerned Japan’s police and Cybercrime Management Middle, together with Oracle, Proofpoint, Resecurity, and US law-enforcement companions. Microsoft mentioned the focused suppliers had been half of a bigger felony community, with associated infrastructure nonetheless being eliminated.
The following problem is limiting how rapidly suppliers can substitute seized domains and compromised accounts. Cloudflare mentioned some area registrars function in jurisdictions that make authorized seizures tough, so it should block entry by means of safety warnings whilst these domains stay on-line.
