
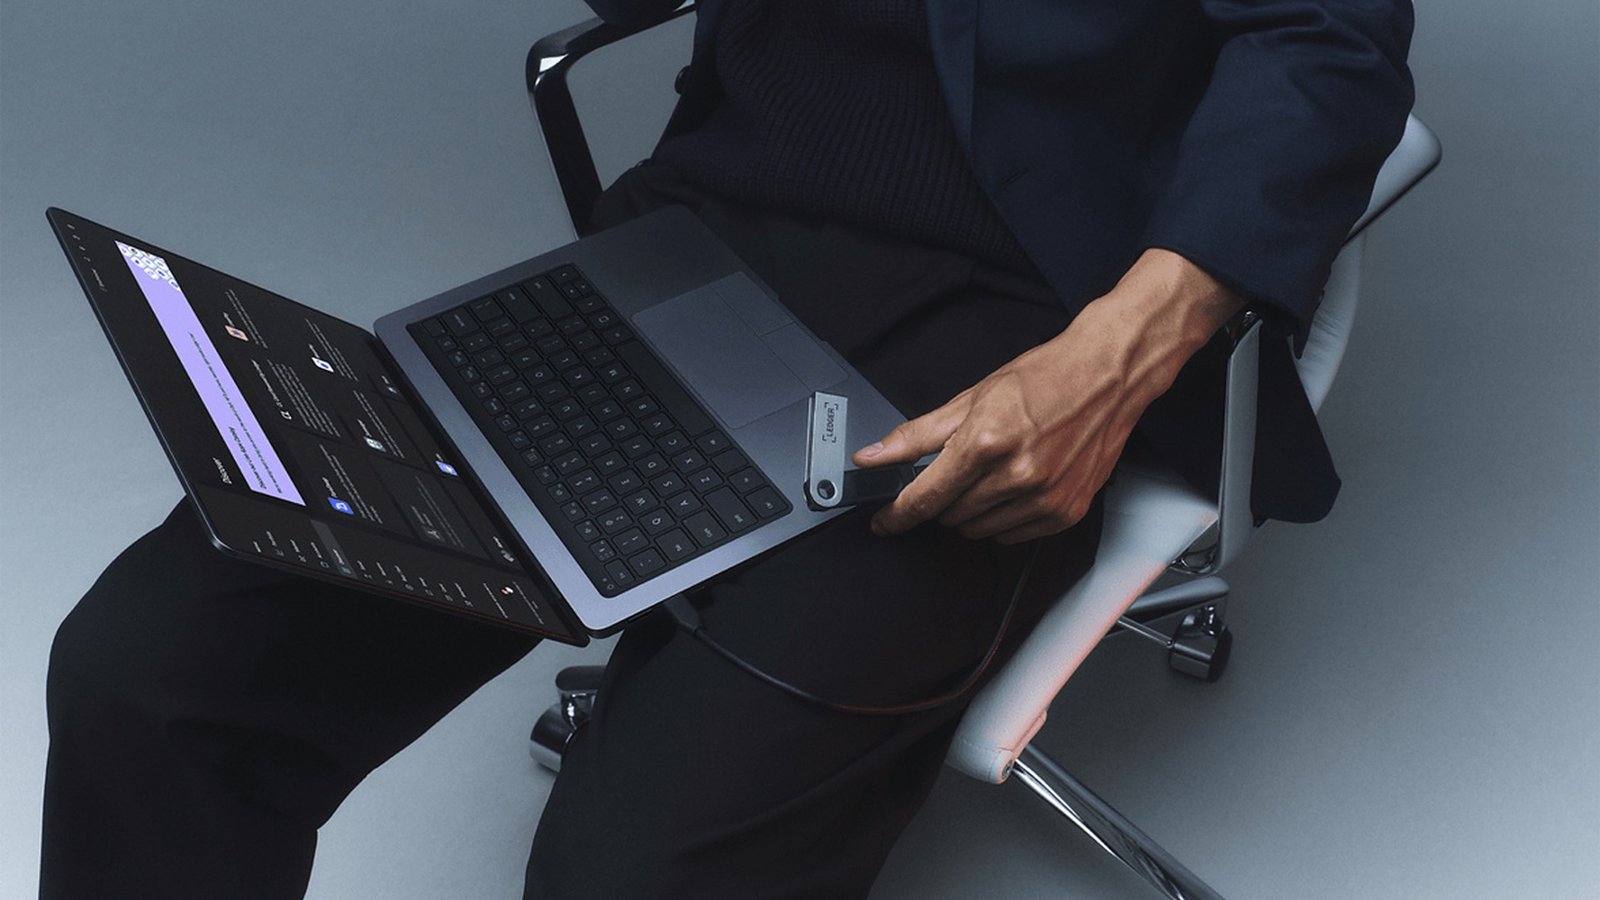
Ledger has stated it’s working with authorities after customers final week reported shedding funds and one obtained a tampered gadget. However the firm reassured clients that the variety of impacted merchandise was “restricted.”
The {hardware} pockets producer added in an announcement on Sunday that it had reached out to affected clients.
Paris-based Ledger on Friday said it had began an investigation after clients in South East Asia reported they’d misplaced funds after shopping for from a reseller.
Then, on Saturday, Ledger said it confirmed that one of many impacted customers’ units contained an unauthorized {hardware} implant.
Ledger wouldn’t verify the amount of cash misplaced however blockchain investigator Specter stated $86 million had been drained from units.
“Because the investigation continues, we’re working with related authorities,” Ledger wrote on Sunday.
It added: “Additionally, we strongly advise customers to not buy from unauthorized resellers, the place the chance of shopping for suspicious, counterfeit or modified units is essential as nothing operates below ledger safety tips.
“Safety isn’t static and this incident underscores why we repeatedly evaluate and strengthen our distribution and anti-tamper processes.”
Clients in South East Asia final week reported shedding funds after shopping for from Kuala Lumpur, Malaysia-based vendor CryptoBilis.
Ledger then suggested clients who’d purchased from CryptoBilis to not arrange their units.
CryptoBilis has since stopped promoting its {hardware} wallets, Ledger stated on Sunday.
Folks on social media posted image proof of units implanted into Ledger merchandise, claiming it might get customers’ personal keys. It isn’t clear what number of of Ledger’s signing units contained the implant.
Neither Ledger nor CryptoBilis instantly responded to questions from Bitcoin Journal.
{Hardware} pockets safety has been a scorching matter ever since hackers in July have been in a position to steal near $120 million in bitcoin from Coldcard customers.
The merchandise, made by Canadian firm Coinkite, contained a firmware bug which led to defective seed technology, permitting hackers to basically guess investor seedphrases.
In a separate incident, {hardware} pockets producer Trezor final month reported that near 81,000 clients had their particulars leaked after its third-party achievement accomplice had knowledge stolen.
Criminals have been concentrating on knowledge this 12 months, with scammers getting maintain of buyer info by way of crypto pockets Ledger’s fee processor International-e to ship phishing emails.
