
AISI started evaluating dangers of the newest frontier AI fashions, previous to their public launch, shortly after it was established in November 2023.
Nevertheless it was reported in September, external that the White Home had requested some main US labs to not share their fashions with the analysis organisation till its personal checks have been accomplished.
The transfer was considered on the time as a blow to AISI – which has been championed by the UK authorities and its companions for advancing open, constructive and collaborative AI testing.
Microsoft president Brad Smith recently told the BBC the institute had helped cement the UK because the nation best-placed to drive ahead world regulation.
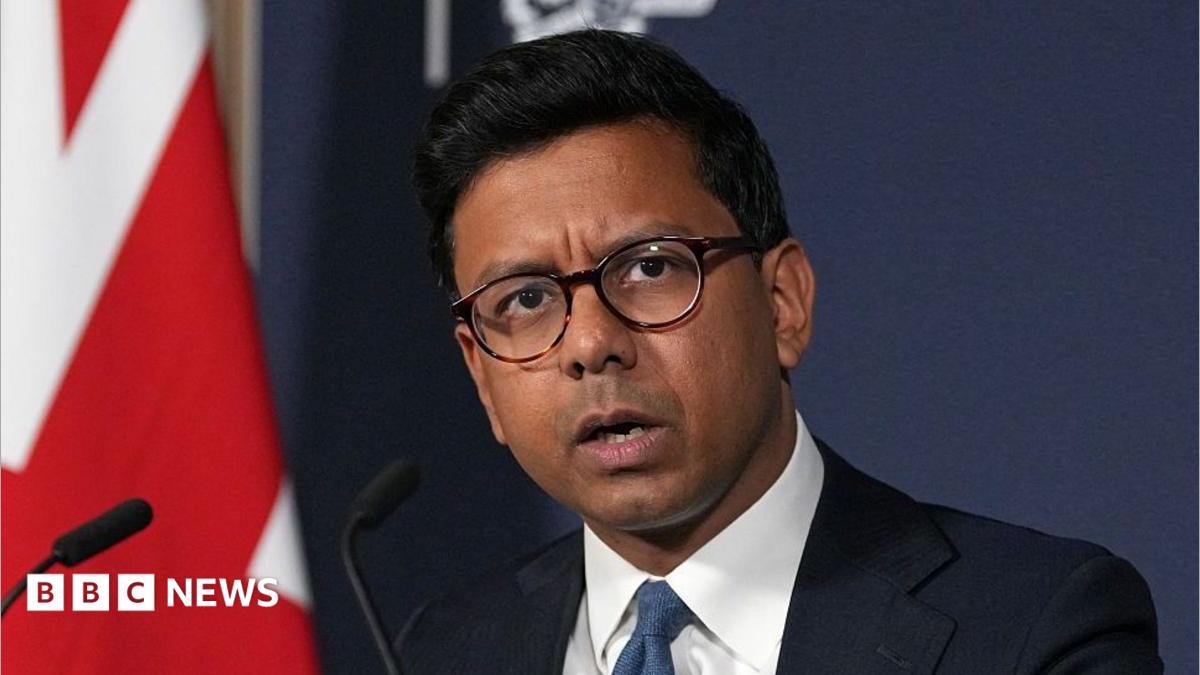
On Monday, Narayan stated that in the previous few weeks, the federal government had labored with the US “to retain entry for Britain’s AISI to essentially the most highly effective AI fashions earlier than they’re launched”.
He additionally stated the UK would additionally look into creating stronger protections by way of the Cyber Safety and Resilience invoice, significantly at how critical AI incidents may be recognized and reported.
The announcement follows a sequence of incidents involving AI brokers throughout major firms such as OpenAI and Anthropic appearing outdoors human management and hacking into exterior techniques.
On 9 September, Evan Hubinger, a prime security researcher at Anthropic, warned in a publish on X that AI is advancing so rapidly he believed there’s a higher than 10% likelihood it “may kill all people” throughout the subsequent decade.
The bosses of the US-based AI giants akin to Anthropic, OpenAI and Google DeepMind have all backed the idea of an AI development slowdown.
Nevertheless, there are presently no world security guidelines in place to control the businesses and their know-how.
In the meantime, President Trump has referred to as for the sector to control itself in order that US corporations don’t lose out to Chinese language rivals.
